Our Clients




Insights
7 min read
How Often Should ODD Be Refreshed? A Practical Framework
Most allocators do a full ODD review every 12 to 36 months, but the right cadence depends on risk. Here's a practical five-step framework for deciding how often to review each manager.
5 min read
Private Equity Has a Cyber Risk Blind Spot
Private equity has become much better at assessing cyber risk, but it may be looking in the wrong place.
7 min read
What AI Actually Changes About the DDQ (and What It Doesn't)
AI is transforming DDQ workflows, but it doesn't change what a questionnaire actually is: self-reported data. Here's where the line falls, and what to ask before adopting an AI-assisted tool.
1 min read
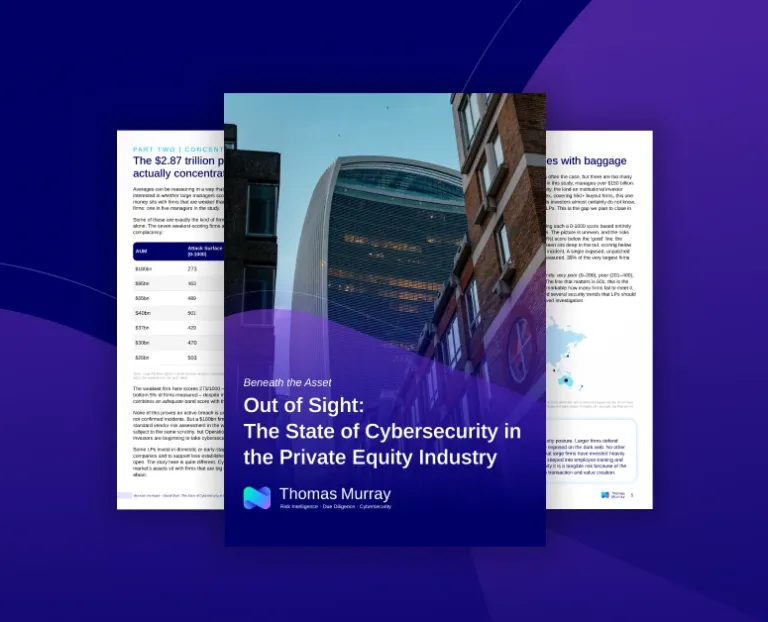
Beneath the Asset – Out of Sight: The State of Cybersecurity in the Private Equity Industry
The UK’s smallest investment funds are weak security link in protecting the IP needed for national growth, new Thomas Murray study finds.