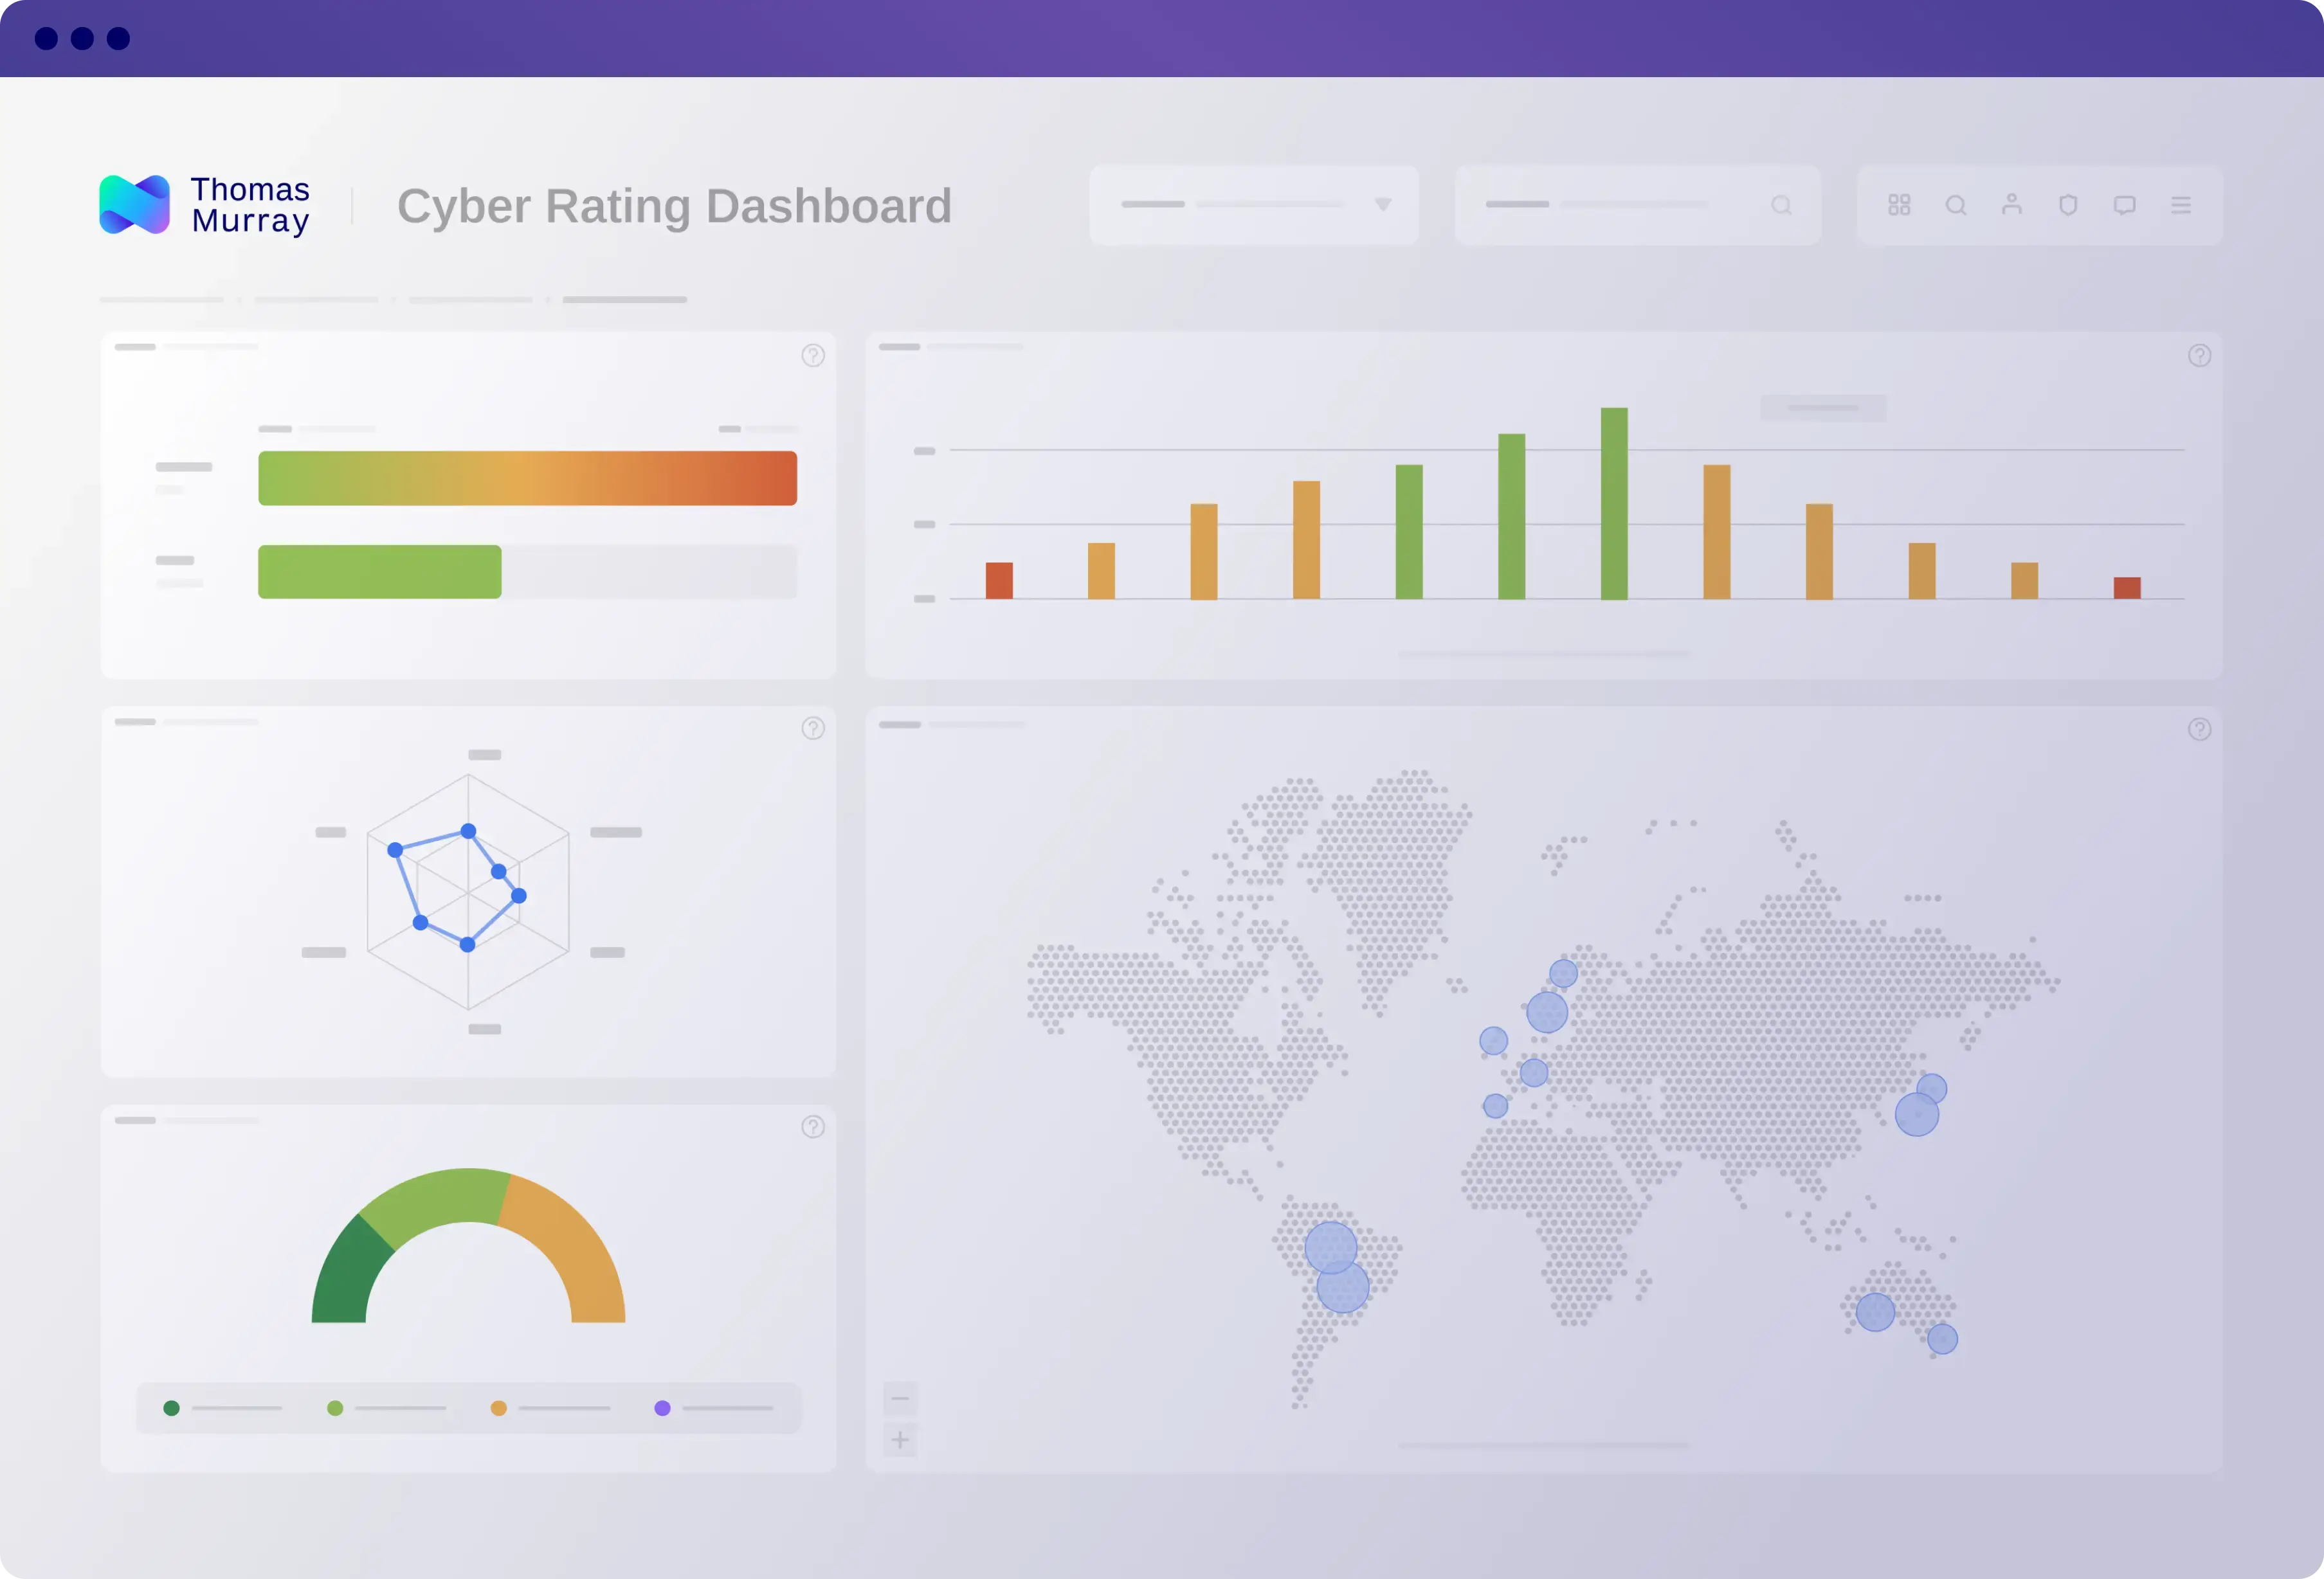
Monitor your third parties continuously with data-driven insight. Assess any organisation’s security using Orbit Security ratings and digital IT security questionnaires, all on one platform.
Your suppliers’ weaknesses are your weaknesses
Every critical supplier, service provider and technology vendor is a potential route into your organisation. A breach at one of them can disrupt your operations, expose your data and damage your reputation, even when your own defences are strong.
Regulators increasingly expect firms to show proactive, documented oversight of third-party risk. Yet many teams still depend on annual questionnaires, spreadsheets and email chains. That’s slow, hard to scale and quickly out of date.
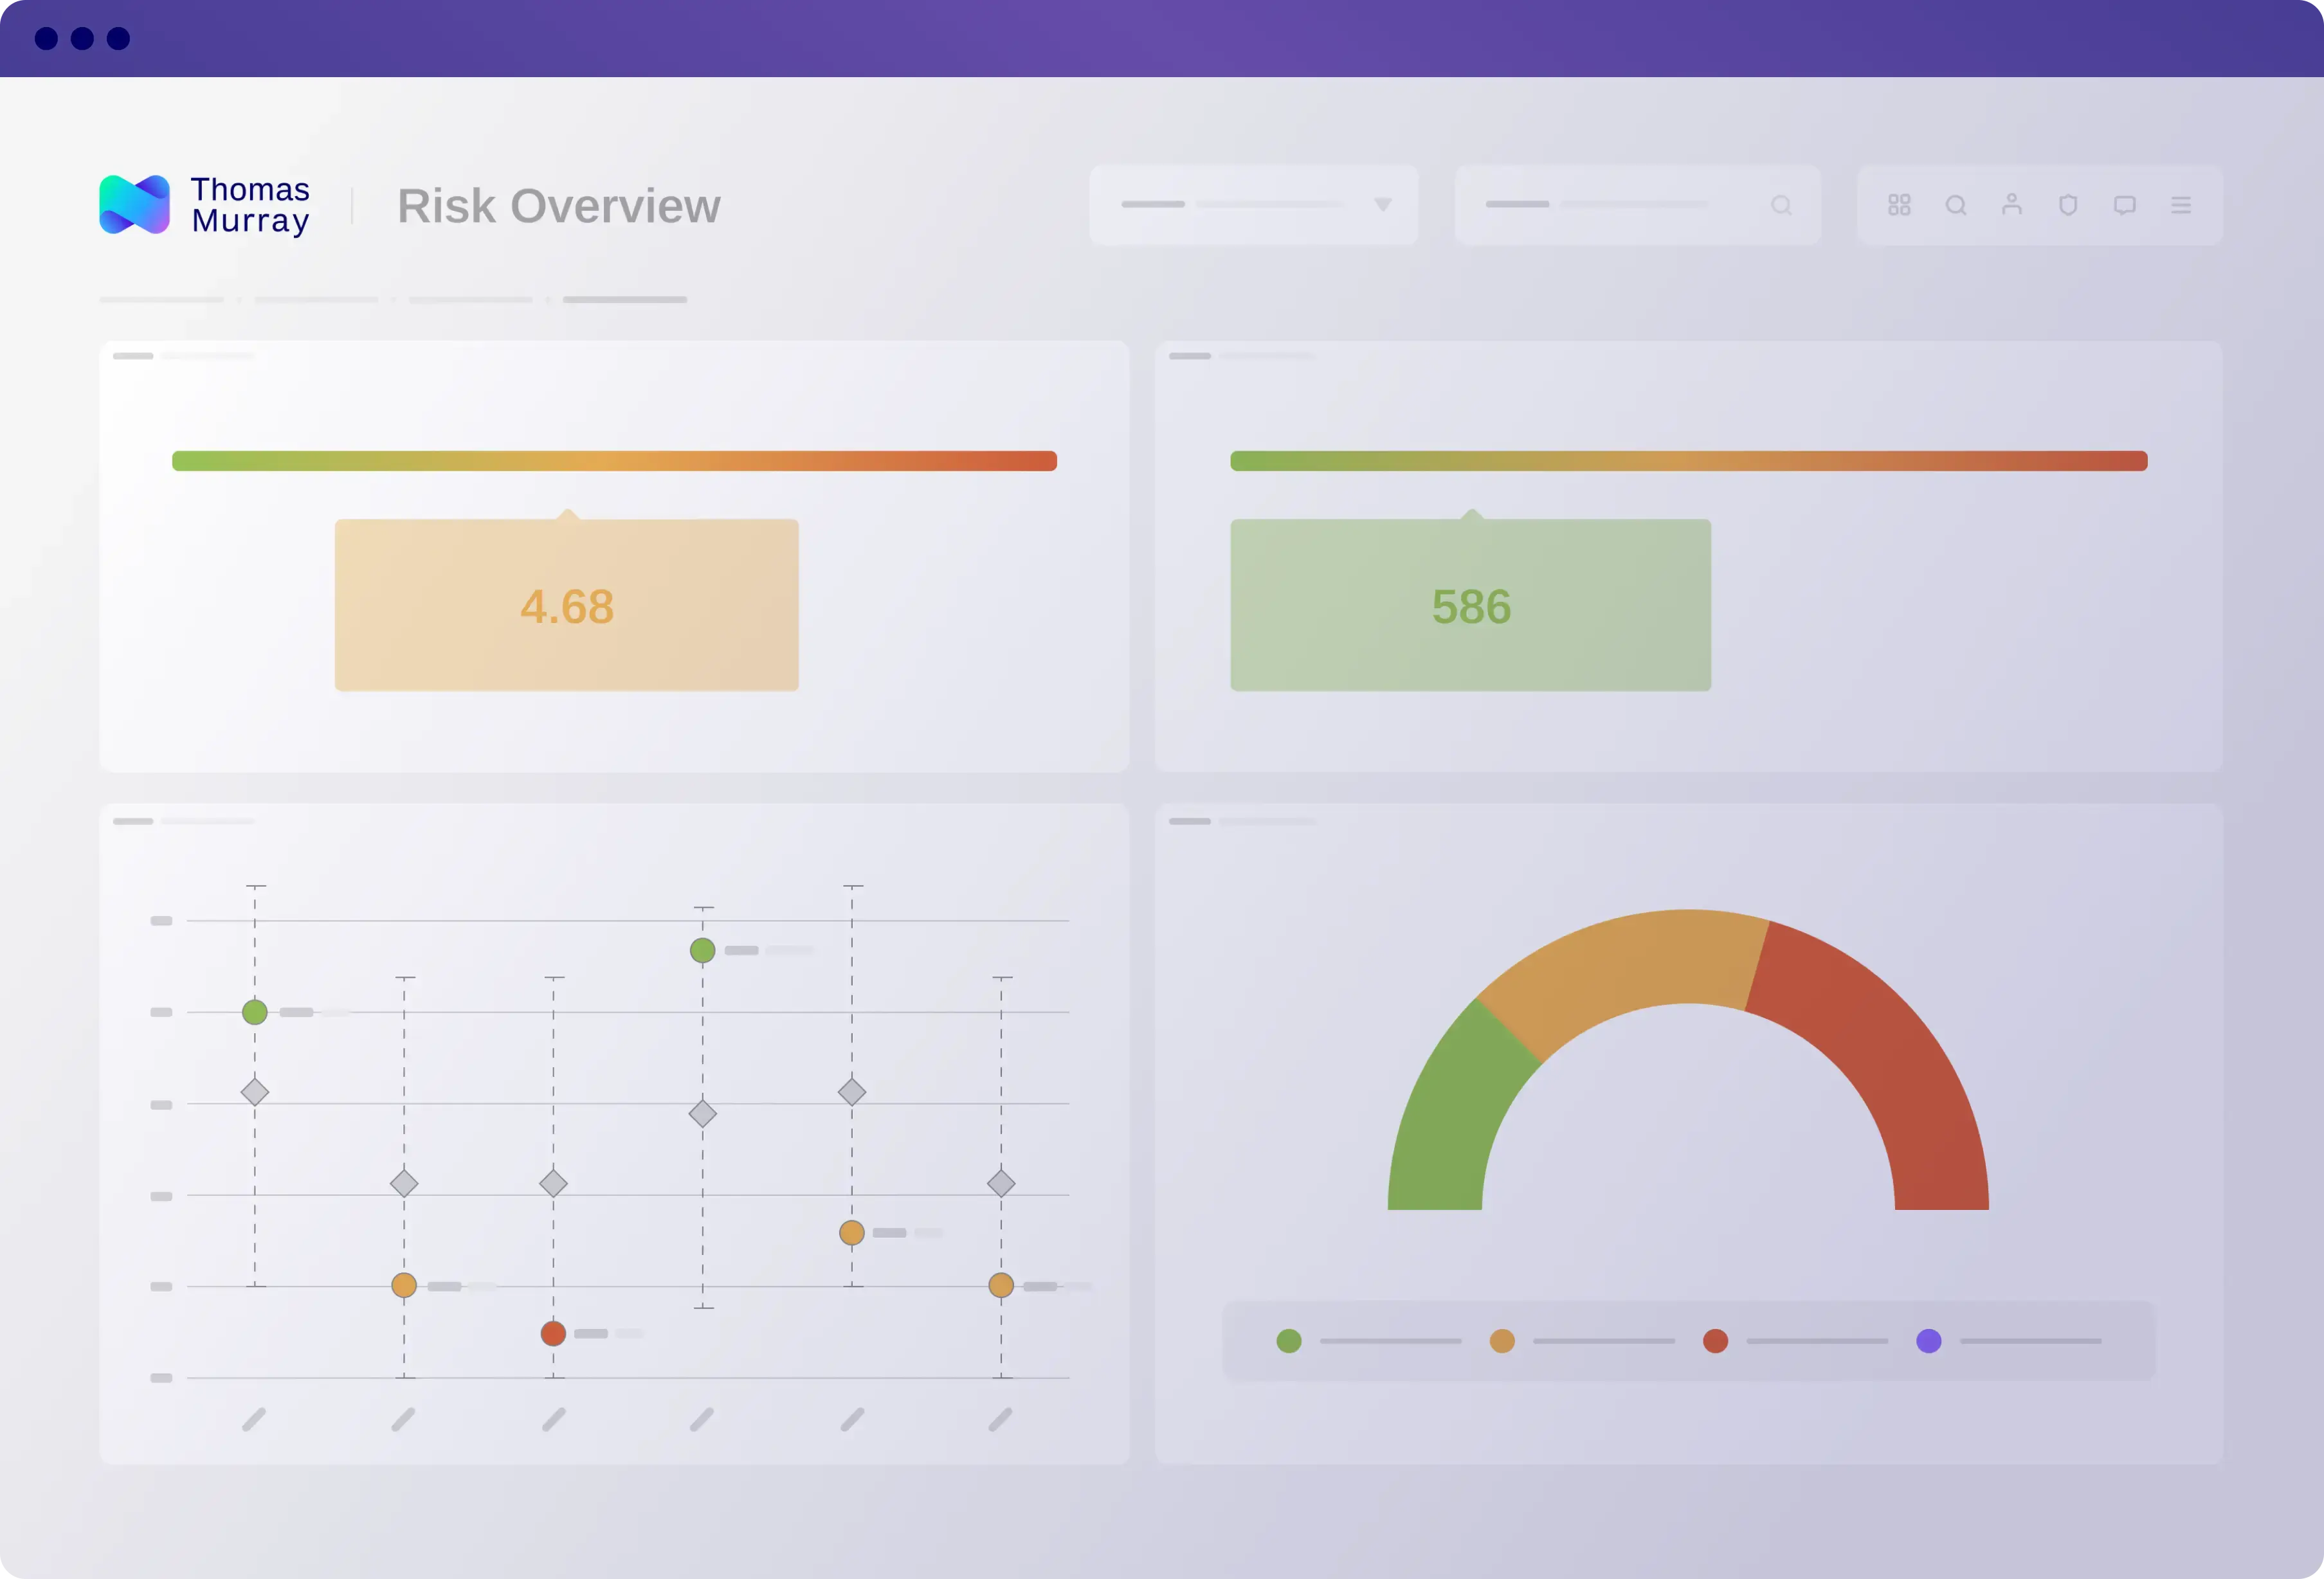
Outside-in ratings and inside-out assessment on one platform
Orbit brings together continuous external security ratings and in-depth IT security questionnaires. You can monitor every critical third party, dig deeper where it matters and help suppliers fix issues, all from one place.
Three steps to stronger third-party security
1. Monitor risk
Spot new vulnerabilities early
See how secure your critical service providers are and know as soon as anything changes.
- Security ratings for your critical providers
- Alerts when new vulnerabilities appear
- Supplier access to their own assessments
- Regular reports for your board and regulators

2. Assess in depth
Go beyond the outside view
Use Orbit Diligence to send IT security questionnaires from Thomas Murray’s library.
- Automated sending and simple workflows
- Automatic scoring of responses
- In-platform messaging with vendors
- Secure document storage and reporting
3. Fix issues fast
Get expert help with fixes
When a third party looks high risk, share its full security rating and threat assessment with it.
- High-impact issues flagged automatically
- Direct support from Thomas Murray’s analysts
- Clear context, so suppliers know what to fix
- All you need to do is make the introduction
Why Orbit
Simplify your vendor risk management
Automated
Combine external security ratings with IT secuirty questionnaires to run a sophisticated monitoring programme without adding to your team's workload.
Centralised
Orbit brings expert security ratings and in-depth due diligence together on one easy-to-use platform, so you can manage all your third-party risk in one place.
Compliant
Built for lean teams facing demanding regulatory requirements. In-depth assessments, tailored reporting and full audit trails help you show regulators a proactive approach to compliance.
What it means for team
Early warning
Get alerted as soon as a supplier’s security worsens.
Depth when you need it
Move from external ratings to detailed questionnaires for your highest-risk suppliers.
Real improvement
Our analysts help suppliers fix issues, not just report them.
Less manual work
Automated questionnaires, scoring and reporting save time for everyone.
Audit-ready
A full audit trail and tailored reports show regulators your oversight.
Take your third-party risk management to the next level
Roland Thomas
Director | Corporate Development, Cyber Risk
Emilia Barnsdale-Ward
Client Relationship Associate | Cyber Risk
Explore our latest insights
Nov 3, 2026
Who Holds the Keys?
When I was a young officer, I learned that no armoury opens to one man. There were two keys, held by...
Nov 2, 2026
Other People’s Networks: What October’s Cyber Incidents Mean for Private Equity
October’s most consequential incidents shared one feature. The point of failure sat outside the vict...
Oct 30, 2026
Binance Hack: $6.3bn Theft Tests Digital Asset Resilience
30 October 2026 — based on information available at the time of writing.